Serious Cybersecurity & IT Consulting for Small-Medium Businesses
Most small businesses know they need better cybersecurity – but don’t know where to start. Blue Leaf provides expert-level cyber security consulting virtual CISO (Chief Information Security Officer) leadership and a clear, framework-based approach using the CIS Controls v8.
Cybersecurity is not “one size fits all”. As a new client, you’ll be guided at the protection level that fits your business today – and grows with you tomorrow.
Our Cyber Security Consulting Process
1. Initial Scope & Context Discovery
We start with a high-level conversation about your business operations, data footprint, and regulatory requirements (like HIPAA, SOC 2, or CMMC). We identify what matters most to your business (your “crown jewels”) so we know exactly what we are protecting.
2. Posture & Vulnerability Assessment
Next, we do a cyber risk assessment and evaluate your current environment – including cloud architecture, network access controls, and employee security awareness – against industry-standard security frameworks (like NIST or CIS Controls).
3. Risk Quantification & Mapping
We translate technical vulnerabilities into business risks. Instead of handing you an overwhelming list of 500 minor bugs, we filter the noise to show you exactly which gaps pose the highest operational, financial, or reputational threat to your company. (If you suspect you’ve already been hacked, then a security incident response & support service would be at the top of your “to-do” list.)
4. Strategic Blueprint Delivery
Finally, we present a prioritized, step-by-step remediation roadmap. We align this directly with your budget and business timeline, giving you a clear picture of what needs to be fixed immediately versus what can needs ongoing management.
That’s our cyber security consulting process in a nutshell.
Here’s how we approach the technical aspects of a new managed security service engagement:
Cyber Hygiene
Find and fix the vulnerabilities attackers exploit most often (the “low hanging fruit”).
Whether you’re a startup with a small team that needs essential, foundational security done right from the get-go, or an established firm looking into a security audit & rehaul, it’s always prudent to start with the basics.
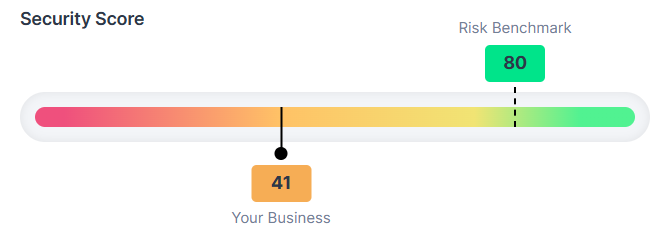
Essential, foundational security controls:
- Cyber Health Assessment (CIS IG1)
- Device & software inventory
- Password/MFA hardening
- Backup & recovery validation
- Secure patch/update policy
- Starter cybersecurity policies
- Employee training
- Annual vCISO review
Best For:
Businesses with 1-50 employees that want strong cybersecurity fundamentals.
Operational Security
Next, upgrade from “basic protection” to full security operations support.
This step is critical for growing organizations or those facing cyber insurance or customer security requirements.
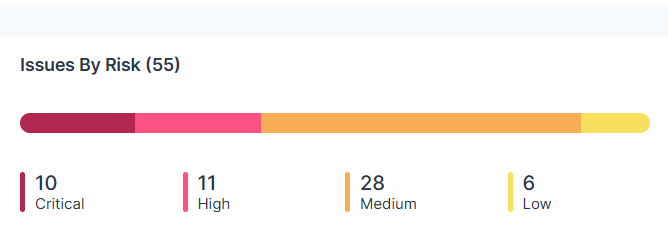
Operational security controls:
- Threat monitoring/MDR oversight
- Email & web threat protection review
- Incident Response Plan + tabletop exercise
- Vendor risk assessments
- Firewall & network configuration review
- Monthly phishing simulations
- Executive-ready quarterly reports
Best For:
Businesses with 25-100 employees needing proactive, ongoing security management.
Strategic Governance
Finally, a full cybersecurity leadership program without the need to hire a full-time CISO.
This is normally required for compliance-driven organizations or those preparing for audits.

Strategic governance controls:
- Formal Cyber Risk Register
- Security metrics & executive dashboards
- Annual penetration test planning/oversight
- CIS → NIST/ISO policy alignment
- Compliance readiness (HIPAA, SOC 2, etc.)
- Board-level reporting
- Quarterly strategic planning sessions
Best For:
Businesses handling sensitive data or operating in regulated industries.
Why Small-Medium Businesses Choose Blue Leaf
We make cybersecurity simple, predictable, and effective.
✔ We use the CIS Controls v8 – the industry’s most proven framework
✔ We explain things in plain English
✔ We deliver expert-level cyber security consulting services
Your security gets stronger every month.
Your risk gets lower every month.
Your business becomes more resilient to cyber threats – and costly downtime.
Ready to Improve Your Cybersecurity?
Get clarity, direction, and expert guidance – with no pressure to buy anything.
Contact me for a free, no-obligation cyber security consulting session today.